Cybersecurity in Georgia and worldwide
Your business.
Reliably
protected.
Let us find the vulnerabilities,
before attackers do.A check today costs less than the consequences tomorrow.
Tbilisi · Working worldwide
THREAT SIMULATION / DEMO
DDoS →
SQLi →
BOT →
DEFENCE SIMULATION
01 — DEFENCE IN DEPTHFrom Georgia, without borders. Reputation and quality first.საქართველო / GEORGIA ↗
KAVKAZ CYBER / SHORT STORY
What a cyberattack looks like — in 32 seconds
A short animated story: from the first attempt to protecting your business.
01 / PHISHING
One click. Unexpected consequences.
The email looks familiar. But its link may lead to a fake sign-in page.
00:00 / 00:32
An illustrative scenario, not a recording of a real attack. Silent animation with explanatory captions.
Discuss your security ↗Video transcript
One click. Unexpected consequences. The email looks familiar. But its link may lead to a fake sign-in page.
A password in the wrong hands. An attacker tries to enter the account. Multi-factor authentication helps stop access.
Your website under pressure. Automated requests can disrupt access for customers. Filtering and rate limits help reduce the risk.
Find weak points before attackers do. Kavkaz Cyber: website assessments, risk reviews and a protection plan. Start with a short consultation.
THREAT LANDSCAPE / SOURCES
Cyber threats: real data
Statistics come from a published Cloudflare report. These are real observations across the Cloudflare network in 2025, not demonstration figures or Kavkaz Cyber results.
Cloudflare · January–December 2025
Daily average: 47,100,000 ÷ 365, rounded. This is the 2025 average, not the number of attacks today.
Source: Cloudflare DDoS Threat Report, Q4 2025 ↗Published: 2026-02-05 · Checked: 2026-11-08 · Report figures do not update automatically.
KAVKAZ CYBER / THREAT SIMULATION
Global cyberthreat globe
A rotating globe with simulated cyberattack routes, right on this page.
GLOBAL THREAT SIMULATIONKAVKAZ CYBER / DIGITAL DEFENCE
DEMO · ATTACK SIMULATIONIllustrative animation: routes and events are simulated. This is not a real-time attack feed or Kaspersky data. Real Cloudflare report statistics appear separately above.
SECURITY ACROSS INDUSTRIES▥ Finance & fintech⌘ IT & technology◇ E-commerce⊞ Small & medium businesses
01 / Our expertise
Security at every
level of your business.
From the first assessment to an incident response plan. We tailor the scope to your infrastructure, risks and goals.
⌕01 / ASSESS
Security audit
An assessment of infrastructure, configurations and processes. A risk overview and an actionable remediation plan.
Discuss an audit ↗⌖02 / TEST
Penetration testing
Testing web applications, networks and APIs within an agreed scope. We show which vulnerabilities could be exploited.
Discuss a pentest ↗⬡03 / PROTECT
Infrastructure protection
Strengthening networks, servers and cloud environments with access controls and secure configurations.
Discuss protection ↗↯04 / RESPOND
Incident response
Help with threat containment, root-cause analysis and recovery. Recommendations to reduce the risk of another attack.
Discuss an incident ↗◎05 / EDUCATE
Employee training
Practical guidance on spotting phishing, handling data safely and protecting user accounts.
Discuss training ↗≡06 / PLAN
Consulting & strategy
Security policies, priorities and a roadmap. We help turn individual measures into a coordinated security programme.
Discuss a strategy ↗03 / OSINT
Open sources.
Evidence-based insights.
When information is abundant but clarity is scarce, verifiable facts matter. Kavkaz Cyber analyses lawfully accessible sources, cross-checks information and helps assess risks before important decisions.
What is OSINT, in plain language?
OSINT means finding and checking information that is already publicly available: on websites, in the news, in listings, reviews and public social media pages.
Think of it as putting together a puzzle. One source gives you a small piece, another gives you one more. We put the pieces together, compare them and explain clearly what we could confirm and what is still unknown.
A simple example
Someone offers you a service and asks for an advance payment. Before sending money, you can check whether the company exists, what public sources say about it and whether the information matches its claims. This helps you spot inconsistencies and make a more informed decision.
We work with information that is lawfully accessible. We do not break into other people's accounts or messages. If information is not public or cannot be reliably verified, we say so clearly.
Your digital footprint
What can people see about you online? At your request, we assess your own public information and exposure risks, and identify protective measures.
Companies and business partners
We review public registers, business publications and available company information to help assess the reliability of a business relationship.
Public information verification
If public claims raise doubts, we compare sources and check inconsistencies and signs of fraud. We distinguish verified facts from assumptions.
The result is a structured report with sources, review dates, limitations and recommendations. The research scope and legal basis are agreed before work begins.
Lawfully accessible information only. No hacking, access to private messages or covert tracking. Complete information or the discovery of personal secrets is not guaranteed.
04 / How we work
Complex threats.
Clear solutions.
Security starts with understanding your business. We agree on the scope and explain our findings, their impact and the next steps.
Confidentiality at every stage01
Understand your needs
We discuss your systems, business processes and what needs protection first.
02
Agree on the plan and scope
We define objectives, testing boundaries, timelines and how we will work together.
03
Assess and recommend solutions
We deliver findings with priorities, supporting evidence and recommendations.
04
Support lasting improvements
We discuss remediation and agree on retesting when needed.
05 / About us
Starting in Georgia.
Looking worldwide.
Kavkaz Cyber is a young cybersecurity company. We work with clients in Georgia and worldwide, with the goal of establishing an international presence and becoming a trusted partner for businesses across countries.
Our highest priority —
reputation and quality of work.
We aim to earn trust through our work: giving every task careful attention, discussing solutions openly and taking responsibility for quality. For us, a company's reputation starts with how it treats its clients.
Discuss your project ↗06 / Frequently asked questions
Start with the essentials.
Where do we start if we have never had an audit?
Start with a discussion of your infrastructure and key risks. This helps identify priority systems and choose the right assessment.
How much does a security assessment cost?
The cost depends on the number of systems, assessment depth and agreed scope. Describe your needs in the form below for an estimate.
Will testing disrupt our business?
We agree on the scope, permitted methods and timing before testing. For critical systems, we separately discuss restrictions and stop procedures.
Can we work remotely?
Yes. We work with companies in Georgia and worldwide. Many tasks, including configuration reviews, web application testing and consulting, can be performed remotely. On-site access needs are determined after discussing your infrastructure.
What will we receive at the end?
Deliverables depend on the service. For audits and penetration tests, you receive a report with findings, risk assessments and remediation recommendations.
07 / Our team
Founder
Kavkaz Cyber.
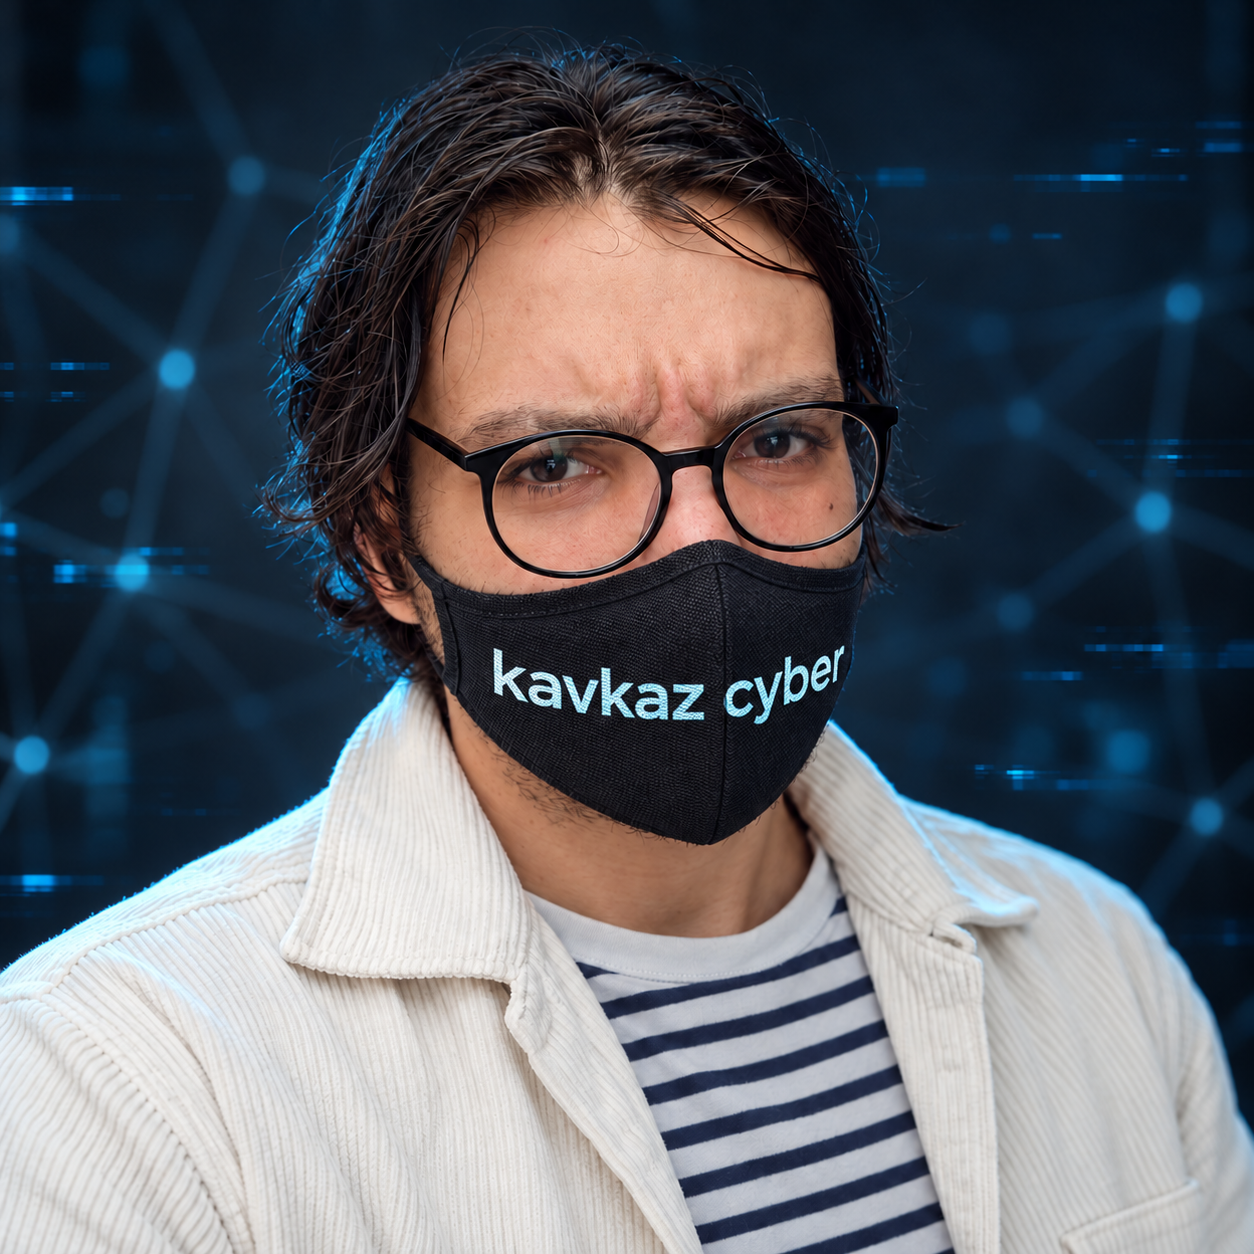
Eduard . P
Director & founder
08 / Short consultation
Let's start with 15 minutes.
Tell us what you want to build, assess or improve. In a short meeting, we will clarify your needs, discuss an approach and identify the next step.
- Choose a topic and preferred time
- We will confirm the meeting by email
- Discuss your needs and next steps
Your proposed time is a preference, not a confirmed booking. The meeting takes place after confirmation. We will share the meeting link or contact method directly.
09 / Consent and review terms
Transparent terms.
Informed consent.
You control your data. An enquiry allows us to contact you; the start and scope of research are agreed separately.
Legal reference: Georgia's Law on Personal Data Protection ↗What data is processed and why?
The Kavkaz Cyber team receives the name, email, company, selected service, enquiry text and consent choices you provide to review your enquiry, respond and discuss a service. Data enquiries: dd.etenish@gmail.com. Providing information is voluntary; without contact details we cannot respond through the form.
For consultation requests, your proposed date, time and time zone are also processed, solely to arrange the consultation.
What does OSINT consent authorise?
The separate optional choice concerns only your own public data for a review you request. The purpose, sources and scope are agreed before work starts. An enquiry or client consent does not authorise hacking, access to private data or unrestricted checks on other people. An appropriate legal basis must be established separately for other people's data.
Retention, withdrawal and your rights
Enquiry data is used until the enquiry and service discussions are completed. If a contract is concluded, retention is specified in it; longer retention requires another lawful basis. You may request information, a copy, correction or deletion and withdraw consent by emailing dd.etenish@gmail.com. Withdrawal does not affect prior lawful processing; further processing requires another legal basis.
How is an enquiry delivered?
The form sends data through FormSubmit to Gmail; these providers may process information outside Georgia under their own terms. Do not submit passwords, documents, sensitive information or other people's personal data through this form. Agree on research details and the transfer of materials separately. A general enquiry does not replace a contract or separate authorisation for technical testing.
10 / Your next step
Let's protect
what you are building.
Tell us about your business and your needs. Start with a brief description, without technical details or confidential information.
Georgia · Tbilisi · Working worldwide
Audit / Protect / Respond
Audit / Protect / Respond